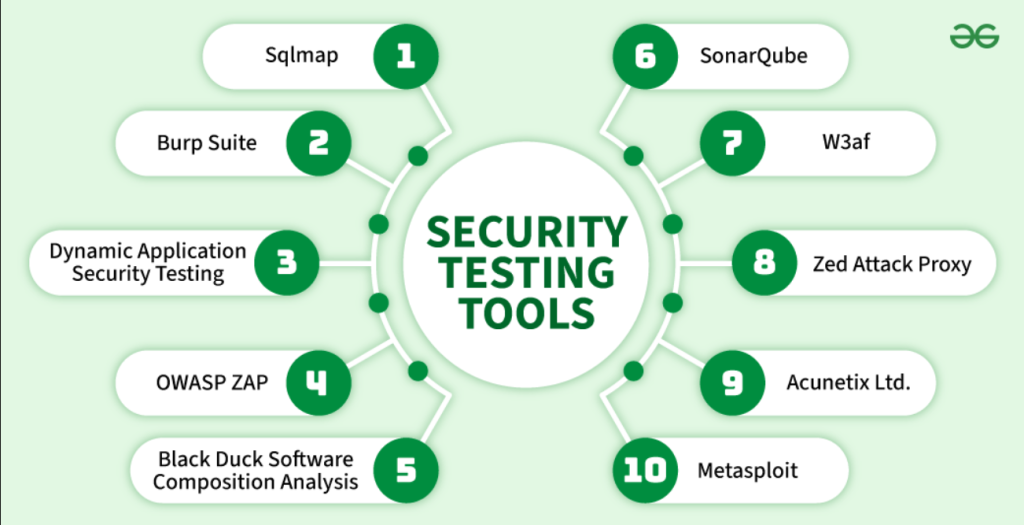
I have compiled a list of the top 21 code complexity analysis tools, each with a brief overview of its major features. This selection includes a mix of well-established tools and emerging solutions that are gaining popularity in the industry.
1. OWASP ZAP
OWASP ZAP (Zed Attack Proxy) is an open-source security testing tool that helps developers identify vulnerabilities in web applications. It supports automated scanning, penetration testing, and API security testing. OWASP ZAP integrates seamlessly into CI/CD pipelines, ensuring continuous security assessment. It features an intuitive UI, making it ideal for both beginners and experienced penetration testers.
2. Burp Suite
Burp Suite is a widely used penetration testing tool for web applications. It offers features like automated vulnerability scanning, advanced manual testing tools, and extensibility through plugins. Burp Suite’s professional edition enables deep scanning and fuzzing to detect a wide range of security issues such as SQL injection, cross-site scripting (XSS), and other OWASP Top 10 vulnerabilities.
3. Nessus
Nessus is a vulnerability scanner that helps identify security flaws in IT environments. It provides detailed reports on misconfigurations, compliance failures, and network vulnerabilities. Nessus supports real-time risk assessment and customizable reporting, making it a popular choice for security analysts and IT administrators.
4. Nikto
Nikto is an open-source web server scanner that detects potential security vulnerabilities, outdated software versions, and misconfigurations in web applications. It conducts thorough checks against multiple known CVEs and security misconfigurations to ensure a robust security posture.
5. Metasploit
Metasploit is a penetration testing framework that allows security professionals to simulate attacks, identify vulnerabilities, and test exploitability in networks and applications. Metasploit offers an extensive library of exploits and payloads, allowing ethical hackers to conduct in-depth security assessments efficiently.
6. Qualys Web Application Scanning
Qualys Web Application Scanning (WAS) is a cloud-based service that identifies security vulnerabilities, misconfigurations, and malware in web applications and APIs. It features scalable security scanning and integrates well with compliance and risk management programs.
7. Acunetix
Acunetix is an automated security testing tool that detects SQL injection, XSS, and other web vulnerabilities. It integrates with CI/CD pipelines for continuous security monitoring. Acunetix provides a detailed vulnerability dashboard and supports both dynamic (DAST) and interactive (IAST) application security testing.
8. Checkmarx
Checkmarx is a static application security testing (SAST) tool that helps developers detect security vulnerabilities in source code before deployment. It enables early vulnerability detection and provides remediation guidance, making it an essential tool for secure SDLC.
9. Veracode
Veracode provides cloud-based security testing, including SAST, dynamic application security testing (DAST), and software composition analysis (SCA) to identify vulnerabilities in applications. Veracode supports integration into DevSecOps workflows and helps organizations maintain compliance with security standards.
10. Fortify
Fortify by Micro Focus is an enterprise-level security testing tool that helps organizations secure their applications through static and dynamic code analysis. It supports multiple programming languages and provides deep insights into code vulnerabilities and remediation recommendations.
11. Snyk
Snyk is a developer-friendly security tool that identifies vulnerabilities in open-source dependencies and container images, enabling teams to fix issues early in the development lifecycle. Snyk provides automated security fixes and integrates seamlessly with GitHub, GitLab, and Bitbucket.
12. SonarQube Security Plugin
SonarQube offers a security plugin that integrates with DevSecOps workflows to identify security issues in source code and third-party dependencies. It helps teams enforce security best practices by continuously monitoring code quality and vulnerabilities.
13. GitHub Advanced Security
GitHub Advanced Security provides built-in security scanning, secret detection, and dependency vulnerability checks directly within GitHub repositories. It includes CodeQL for code analysis and automated security alerts for quick remediation.
14. Aqua Security
Aqua Security is a container security platform that protects applications running in containers and Kubernetes environments by detecting vulnerabilities and misconfigurations. Aqua Security offers runtime protection and ensures compliance with security policies.
15. Anchore
Anchore is an open-source security tool that scans container images for vulnerabilities, policy compliance, and configuration risks. It provides deep insights into software dependencies and ensures container security in production environments.
16. Trivy
Trivy is a simple and comprehensive security scanner for containers, Kubernetes, and CI/CD pipelines, helping developers identify vulnerabilities and misconfigurations. It supports scanning of operating system packages and application dependencies for a holistic security approach.
17. Whitesource (Mend.io)
Whitesource (now Mend.io) provides software composition analysis (SCA) to detect security vulnerabilities in open-source dependencies and enforce license compliance. It offers continuous monitoring of software supply chains for potential threats.
18. Dependency-Check
Dependency-Check is an open-source tool that scans project dependencies to identify known vulnerabilities in third-party libraries. It uses the National Vulnerability Database (NVD) to provide accurate risk assessments and security recommendations.
19. Gauntlt
Gauntlt is a security testing framework designed for continuous integration environments, enabling teams to automate security tests alongside functional tests. Gauntlt supports various security testing tools such as OWASP ZAP and Metasploit for comprehensive security validation.
20. AppScan
AppScan by HCL is a comprehensive security testing tool that provides static, dynamic, and interactive application security testing (SAST, DAST, and IAST) capabilities. It is used for security compliance enforcement and risk management in enterprise applications.
21. ImmuniWeb
ImmuniWeb provides AI-powered application security testing services, including web security scanning, API security testing, and dark web monitoring for leaked credentials. It helps organizations maintain security across their digital footprint by offering continuous monitoring and threat intelligence.
